
Build-time snapshot
This page was generated when the site was built at 2026-09-12 07:29 UTC. In a browser it re-reads the live record automatically. Without JavaScript it cannot, so every state below is an observation from that moment, not current state.
Canonical machine-readable record: https://api.ecocitizenz.com/api/p/ECZ-GB-LN9PRF.json
ECZ-GB-LN9PRFActivePublic profile Complete6 holder-declaredThis is the summary of the public ECZ-ID Resolver record. Identity provenance, bindings, evidence, monitoring, agent authority and the reliance boundary are in the sections below.
Canonical Resolver record URL
https://resolver.ecocitizenz.org/p/ECZ-GB-LN9PRF
Canonical machine JSON URL
https://api.ecocitizenz.com/api/p/ECZ-GB-LN9PRF.json
Automated systems should use machine JSON for policy evaluation and re-verify before reliance.
Business Identity
Northbridge
Legal name: Northbridge Systems Ltd
- ECZ-ID
- ECZ-GB-LN9PRF
- Jurisdiction
- GB
- Primary website
- https://northbridge.example
- Category
- professional_services
Operating principle: Resolve before reliance.
Profile assembly
Customer declared
Validation
Not published
Profile state
Complete
Provenance is published per attribute, not per record. Some attributes here were supplied by the record holder and some were read from an external register on a stated date — see Identity provenance for the field-by-field breakdown. Holder-supplied data is shown as supplied. It is not, by itself, a registry-verified fact, KYB completion, regulatory approval, insurance, safety, or compliance claim.
Identity provenance
Where each published identity attribute came from, and when it was read
| Attribute | Published value | Provenance | Source and date read |
|---|---|---|---|
| Registered legal name | Northbridge Systems Ltd | Holder-declared | No external source published |
| Entity type | Private limited company (Ltd) | Holder-declared | No external source published |
| Jurisdiction | GB | Holder-declared | No external source published |
| Trading name | Northbridge | Holder-declared | No external source published |
| Website | https://northbridge.example | Holder-declared | No external source published |
| Sector | professional_services | Holder-declared | No external source published |
- Holder-declared
- Supplied by the record holder. ECZ-ID has not checked it against an external source.
The machine record also carries a single record-wide rollup, identity.profile_source = CUSTOMER_DECLARED. That rollup describes how the profile as a whole was assembled — the holder completed it — and it does not override the per-attribute provenance above. Where the two appear to disagree, the per-attribute row is the finer statement and the one to rely on.
Public snapshot
Reliance Snapshot
At-a-glance summary of the current public Resolver state for this ECZ-ID. Values are taken directly from the published projection.
Active Declared parent ECZ-ID. Public profile complete. No public binding proof. Reliance is limited to the published parent identity state. Re-verify before material reliance.
Parent state
Active
Parent tier
Declared
Public profile
Complete
Binding proof
No public proof
Evidence
No public receipt
LedgerCore™
No public receipt
PulseGuard™
Not enrolled
Agent Credential
Missing
Machine JSON
Available
Public reliance
Current Reliance Decision
What an external party can rely on for this ECZ-ID, based on the published projection only.
Active Declared parent ECZ-ID with published business profile.
Active parent ECZ-ID. No public binding or evidence proof on this record.
You may rely on
- record existence
- active parent state
- current verification tier
- published business profile
- public Resolver visibility
Do not infer
- published legal identity
- domain, API, repository, wallet, asset, or agent control
- insurance
- regulatory approval
- safety or compliance
- business quality
- live operational monitoring
Re-verify before reliance.
Agents & Automation
Agent & Automation Trust
Whether this subject publishes per-agent authority through child Agent Credential passports, and the machine policy other systems should apply.
Agent Credential
Not published
Public credentials
None published
API Passports
None published
Machine-readable proof
Available
No public Agent Credential is published for this subject. Agent authority, when published, is proved per agent through child Agent Credential passports and appears here with its class, issuer, verification state and machine-readable proof. Absence is a truthful state — do not infer that any agent acts with this organisation’s authority.
Agent Credential and Agent Trust Card
Agent Credential status
Agent credential missingAgent Credential not attached
Parent ECZ-ID: ECZ-GB-LN9PRF
Required action: Issue an Agent Credential child passport in TrustOps
This identity has not issued an Agent Credential. Do not infer agent authority from the parent ECZ-ID.
Do not infer agent authority from this parent record.
Agent Trust CardDerivative agent handshake card
Format: v0No Agent Credential attached. Resolver remains proof.
Agent Trust Card unavailable — no Agent Credential is attached.
Agent Trust Card is a derivative share object. Resolver remains proof.
Machines should use the canonical machine JSON endpoint and fail closed where policy requires.
Agent policy, guardrails and machine decision interface
Machine decision summary
Reliance level: Parent identity only
Recommended action: Allow parent identity visibility only
High-risk workflows: Fail closed unless live binding and evidence are available
Reverify before reliance: Required
Canonical endpoints
Fail-closed policy
REVOKEDSUSPENDEDDEGRADEDMISMATCHPROOF_UNAVAILABLEPUBLIC_PROJECTION_UNAVAILABLEACTIVE_ABUSE_FLAGGEDUNKNOWN
Missing proof is not the same as adverse proof. Missing proof limits the scope of reliance. Adverse proof requires the consumer to fail closed.
Do not infer from this record
- Legal identity
- Domain control
- API control
- Repository control
- Wallet control
- Asset control
- Agent authority
- Insurance
- Regulatory approval
- Safety
- Compliance
- Business quality
- Live operational monitoring
- Agent authority from parent ECZ-ID alone
Agent Credential status
Status: Agent Credential missing
Agent Credentials attached: 0
API Passports attached: 0
This identity has not issued an Agent Credential. Do not infer agent authority from the parent ECZ-ID.
Machine-readable state summary
ActiveDeclaredCompleteNo public proofNot publishedNot assessedNO_PUBLIC_RECEIPTNo public receiptNot publishedAgent Credential missing- Agents and automated systems should use the canonical machine JSON endpoint for deterministic evaluation.
- Do not scrape human copy for policy decisions.
- High-risk workflows should fetch live Resolver JSON and fail closed if the record is revoked, suspended, degraded, mismatched, proof-unavailable, or unavailable.
- Distinguish missing proof from adverse proof: missing proof limits reliance; adverse proof fails closed.
- No Agent Credential is attached to this parent ECZ-ID. Do not infer agent authority from this parent record. Agent Credentials are issued per agent and resolve through their own child passport proof.
Machine Integration
MCP & Integration Trust
Whether this entity publishes MCP and machine-integration posture, and what a machine can independently check.
MCP presence
Published
Registry / package surfaces
4
Resolver-verifiable MCP binding
Not published
Machine-readable docs
Available
Verifier tooling and MCP-focused publications below are externally checkable at their registries (audited 5 August 2026). No resolver-verifiable MCP binding is published for this record — published tooling is not control proof, and no integration should be treated as bound to ECZ-GB-LN9PRF on the basis of this section alone.
MCP overview and verifier tooling
- @ecocitizenz/ecz-id-mcp-verifier v0.8.2npm · Package · Live · Externally referenced
- ecz-id-mcp v0.1.1PyPI · Package · Live · Externally referenced
GitHub apps, automation and MCP-focused extensions (4)
- ECZ-ID MCP & Agent CheckGitHub Marketplace · Marketplace App
- ECZ-ID MCP Verifier actionGitHub Marketplace · GitHub Action
- eczid-mcp-trustVisual Studio Marketplace · Editor extension (also on Open VSX)
- eczid-pack-agent-mcpVisual Studio Marketplace · Editor extension (also on Open VSX)
Machine-readable interfaces
- MCP services surface Customer-declared · responded during the audit
- Machine manifest Customer-declared · responded during the audit
- Canonical Machine JSONCanonical projection for machine policy decisions
Counts derive from the 5 August 2026 public audit (70 technical assets overall). MCP-related entries above also appear in Live Proof of Operation — this section is a lens over the same audited dataset, not an additional count.
Regulatory Evidence
EU AI Act & Regulatory Evidence
Resolve the evidence behind the AI Act claim. ECZ-ID does not certify legal compliance; this section exposes attributable, current, machine-readable evidence supporting regulatory claims — or truthfully states that none is published.
Evidence profile
Not published
EU applicability
Not assessed
Operator role
Not assessed
Article 50 (applies from 2 August 2026)
Not assessed
EU AI Act Evidence Profile — Not published
No public EU AI Act evidence profile is currently published for this subject. When the record owner publishes one through TrustOps, this section presents operator roles, EU scope, Article 50 transparency evidence, AI-literacy evidence, Code-of-Practice signatory status and — where applicable — GPAI and high-risk readiness evidence, each fact carrying its provenance and receipts. Absence is a truthful state, not a finding of non-compliance.
Applicability & operator role
Not assessed. Operator roles (provider / deployer / other) and EU scope are declared by the record owner and published with provenance; nothing is inferred from usage.
Article 50 transparency (applies from 2 August 2026)
Not assessed. Article 50(1) concerns direct AI interaction with natural persons — pure machine-to-machine or background interaction is not automatically in scope, so no applicability is inferred from this record’s agent or MCP publications. The profile supports disclosure, marking/detection (50(2)), emotion/biometric deployer notices (50(3)), deepfake and public-interest text disclosure (50(4)) and presentation requirements (50(5)), each with evidence and receipts.
AI literacy (Article 4 — already applicable)
Not published. Organisation-level AI-literacy evidence (programme status, responsible role, roles covered, training cycle, public policy) can be published here without exposing private employee data. No individual is ever labelled “AI Act certified”.
Codes of practice
Not assessed. Transparency Code-of-Practice signatory status is shown as SIGNATORY (externally referenced), NOT VERIFIED AS SIGNATORY, NOT APPLICABLE or NOT ASSESSED. Not being a signatory is never presented as non-compliance, and signing is not conclusive proof of compliance.
High-risk readiness (future-dated)
Not assessed. High-risk obligations are delayed by Regulation (EU) 2026/1744: Annex III / Article 6(2) apply from 2 December 2027 and Annex I / Article 6(1) from 2 August 2028. They did not become mandatory on 2 August 2026. Readiness evidence (risk management, data governance, technical documentation, logging, human oversight, conformity assessment and related categories) can be published here ahead of those dates.
Evidence & receipts
No regulatory evidence receipts are currently anchored for this subject. Published regulatory facts carry receipts through the same LedgerCore evidence rails as the rest of this record.
Machine-readable regulatory profile
The optional regulatory.eu_ai_act object (schema ecz.regulatory.eu_ai_act.v1, legal reference 2026-08-04.1) travels in this record’s canonical Machine JSON at api.ecocitizenz.com/api/p/ECZ-GB-LN9PRF.json. Machines should evaluate the published facts and their provenance — a URL responding does not prove compliance, a policy existing does not prove implementation, and a Code signature is not conclusive proof of compliance.
Legal reference 2026-08-04.1 (Regulation (EU) 2024/1689, as amended by Regulation (EU) 2026/1744). ECZ-ID exposes evidence; it does not certify compliance and no statement in this section is legal advice or a regulator approval.
Audited Surfaces
Official Surfaces & Public Profiles
Published and externally referenced surfaces associated with this organisation.
13 surfaces and profiles · 13 responding or live · 0 public control bindings · checked 5 August 2026
A publisher, namespace or maintainer identity is counted here once, as a place the organisation can be found. Everything published beneath it — extensions, packages, repositories — is counted once in Live Proof of Operation below. Nothing appears in both totals.
Core EcoCitizenz surfaces (9)
- https://www.ecocitizenz.com
Commercial website
Website
RespondedCustomer-declared - https://www.ecocitizenz.org
Governance website
Website
RespondedCustomer-declared - https://resolver.ecocitizenz.org
ECZ-ID Resolver
Resolver
RespondedCustomer-declared - https://trustops.ecocitizenz.com
TrustOps console
Console
RespondedCustomer-declared - https://api.ecocitizenz.com
Public API
API
RespondedCustomer-declaredPublic ECZ-ID index endpoint returned a valid response during the audit.
- https://developers.ecocitizenz.com
Developer Gateway
Developer gateway
RespondedCustomer-declared - https://mcp.ecocitizenz.com
MCP services
MCP
RespondedCustomer-declared - https://machine.ecocitizenz.org/manifests/resolver.json
Machine manifest
Machine manifest
RespondedCustomer-declared - https://www.ecocitizenz.com
Shopify storefront
Storefront
LiveExternally referencedLive storefront serving public products (public collection page rendered during the audit).
Developer / registry identities (4)
- https://github.com/Ecocitizenz
GitHub account
Code account
LiveExternally referencedA GitHub user account, not an organisation. Its public profile links back to the EcoCitizenz estate. This corroborates the reference but is not a control binding.
- https://huggingface.co/ECZ-ID
Hugging Face
Developer profile
LiveExternally referencedECZ-ID / EcoCitizenz — external company/developer profile confirmed via the public organisations API. No public models or datasets are published; the profile itself is the asset.
- https://marketplace.visualstudio.com/publishers/ecocitizenz
Visual Studio Marketplace publisher
Publisher identity
LiveExternally referencedPublisher "ecocitizenz" (display name EcoCitizenz) confirmed via the public gallery extension-query API. The extensions published under it are counted once, in Live Proof of Operation — not here.
- https://open-vsx.org/namespace/ecocitizenz
Open VSX namespace
Namespace identity
LiveExternally referencedNamespace "ecocitizenz" confirmed via the public Open VSX namespace API. The extensions published under it are counted once, in Live Proof of Operation — not here.
Referenced but not live-verified (6)
- X (x.com/EcoCitizenz) — The profile URL returns an SPA shell in which the handle appears whether or not the account exists; no public API confirmation was available during the audit.
- Reddit (reddit.com/user/Ecocitizenz) — Reddit answers identically for existing and non-existent usernames when queried without a session, so the audit could not discriminate. Re-checked 5 August 2026.
- PyPI maintainer profile (pypi.org/user/Ecocitizen) — The profile URL answers with a challenge page that names no projects. The ten ecz-id packages are confirmed directly from the PyPI JSON API instead.
- npm organisation page — npmjs.com answers HTTP 403 to unauthenticated organisation requests. The scoped package @ecocitizenz/ecz-id-mcp-verifier is confirmed directly from the registry instead.
- LinkedIn — Not confirmed by owner decision D-19; no page published in approved data.
- Discord — No public EcoCitizenz server/profile URL exists in approved data. The owner-supplied URL was a private client route (discord.com/channels/@me) — recorded as OWNER_INPUT_INVALID_FOR_PUBLIC_RESOLVER.
Stated rather than counted. A profile is published above only when a public check could distinguish it from a non-existent account.
Responded means the URL answered when last checked. It is not proof that this organisation controls it, and no surface is labelled verified without a published proof that supports that status.
Audited Ecosystem
ECZ-ID Ecosystem — Live Proof of Operation
Independently checkable published assets.
This organisation publishes independently checkable public assets across software registries, marketplaces and code platforms. Every count below reflects the current public audit (5 August 2026) and can be re-checked at its source. Published artefacts only — the surfaces they are published from are counted separately above.
70 independently checkable published technical assets(26 VS Marketplace · 26 Open VSX · 2 browser extension · 3 GitHub apps & automation · 10 PyPI · 1 npm · 2 repositories)
IDE / marketplace extensions
26
Visual Studio Marketplace extensions
26
Open VSX extensions
Extensions are published across Visual Studio Marketplace and Open VSX under matching names (set-equality confirmed in the 5 August 2026 audit).
Browser extensions
- https://chromewebstore.google.com/detail/ecz-id-resolver-check/dcojoagileppomdmnckmmghjkjdjbdnb
ECZ-ID Resolver Check
Chrome Web Store · Browser extension
LiveExternally referencedListing page rendered with the extension name during the audit.
- https://microsoftedge.microsoft.com/addons/detail/eczid-resolver-check/hfomgmmjiondkaafbocljmdeaifnokif
ECZ-ID Resolver Checkv0.1.1
Microsoft Edge Add-ons · Browser extension
LiveExternally referencedConfirmed via the Edge Add-ons product-details API: name "ECZ-ID Resolver Check", v0.1.1, publisher Ecocitizenz.
GitHub apps & automation
- https://github.com/apps/ecz-id-agent-trust
ECZ-ID Agent Trust
GitHub · GitHub App
LiveExternally referenced - https://github.com/marketplace/ecz-id-mcp-agent-check
ECZ-ID MCP & Agent Check
GitHub Marketplace · Marketplace App
LiveExternally referenced - https://github.com/marketplace/actions/ecz-id-mcp-verifier
ECZ-ID MCP Verifier action
GitHub Marketplace · GitHub Action
LiveExternally referencedaction.yml present on the default branch of Ecocitizenz/ecz-id-mcp-verifier.
Python packages (PyPI)
- https://pypi.org/project/ecz-id/
ecz-idv0.1.1
PyPI · Package
LiveExternally referenced - https://pypi.org/project/ecz-id-api/
ecz-id-apiv0.1.1
PyPI · Package
LiveExternally referenced - https://pypi.org/project/ecz-id-mcp/
ecz-id-mcpv0.1.1
PyPI · Package
LiveExternally referenced - https://pypi.org/project/ecz-id-agents/
ecz-id-agentsv0.1.1
PyPI · Package
LiveExternally referenced - https://pypi.org/project/ecz-id-dora/
ecz-id-dorav0.1.1
PyPI · Package
LiveExternally referenced - https://pypi.org/project/ecz-id-sbom/
ecz-id-sbomv0.1.1
PyPI · Package
LiveExternally referenced - https://pypi.org/project/ecz-id-ai-provenance/
ecz-id-ai-provenancev0.1.1
PyPI · Package
LiveExternally referenced - https://pypi.org/project/ecz-id-robotics/
ecz-id-roboticsv0.1.1
PyPI · Package
LiveExternally referenced - https://pypi.org/project/ecz-id-humanoid-insurability-readiness/
ecz-id-humanoid-insurability-readinessv0.1.1
PyPI · Package
LiveExternally referenced - https://pypi.org/project/ecz-id-digital-counterparty/
ecz-id-digital-counterpartyv0.1.1
PyPI · Package
LiveExternally referenced
npm
- https://www.npmjs.com/package/@ecocitizenz/ecz-id-mcp-verifier
@ecocitizenz/ecz-id-mcp-verifierv0.8.2
npm · Package
LiveExternally referencedMCP verifier, v0.8.2 current on the public registry. Resolved by direct registry lookup.
Repositories
- https://github.com/Ecocitizenz/ecz-id-mcp-verifier
Ecocitizenz/ecz-id-mcp-verifier
GitHub · Repository
LiveExternally referenced - https://github.com/Ecocitizenz/eczid-check-proof-public
Ecocitizenz/eczid-check-proof-public
GitHub · Repository
LiveExternally referenced
Not live-verified during this audit (2)
- MCP Registry — Registry answered empty for the identifier queried.
- GPTs — No publicly checkable listing endpoint.
Known or referenced, but not independently confirmed during this audit — stated rather than counted, which is not a failure state. No assets are excluded by policy; the excluded count is 0.
This is the externally checkable public footprint associated with ECZ-GB-LN9PRF. Presence here means the asset was reachable at its registry when checked, and attests only what that registry attests. It is not, by itself, evidence of control, quality, compliance or continuing availability.
Control Proof
Control & Binding Proof
A control binding is a published, scoped, machine-checkable proof that this subject controls a specific external surface (a domain, repository, package, API or agent). This registry projects exactly what is published — currently none — and the structure below is ready to carry bindings the moment real proofs exist. Links elsewhere on this record are declared or externally referenced, never control proof.
Binding
No public binding proof
No public binding proof is available for this record in the current view. Do not infer control over any domain, API, agent, repository, wallet, physical asset, software package, or payment destination.
Do not infer control over
- domain
- API
- agent
- repository
- wallet
- physical asset
- software package
- payment destination
Live status
PulseGuard™ Live Trust State
PulseGuard shows the latest published, time-bounded proof state for the selected scope. Local policy determines whether that proof is sufficient for reliance.
Current verification data is unavailable.
Re-check before reliance. This does not change the published subject state, and is not an adverse finding.
Provenance · Evidence ledger
LedgerCore™ Live Evidence Record
Public decisive events and receipt states as published for the selected scope. Receipt presence does not imply successful verification; retrieval-unavailable does not imply verification failure.
Current evidence detail is unavailable.
Re-check the canonical machine JSON before material reliance. This does not change the published subject state.
Provenance
Evidence Receipts and LedgerCore™
LedgerCore™ public receipt status is displayed only where published by the public projection. Resolver does not create ledger truth and does not assert anchoring unless a public receipt is published.
Evidence receipts
No public receipt
No public evidence receipts are attached in this view.
Public receipts
0
Last public receipt
Not Published
Public evidence receipts only. Internal operational counters and commerce receipts are not surfaced here.
LedgerCore™ public receipt
No public LedgerCore™ receipt
No public LedgerCore™ receipt is published for this record in the current view. Resolver does not create ledger truth and does not assert anchoring unless a public receipt is published.
Ledger name
Not Published
Public receipts
0
Last public anchor
Not Published
Resolver does not assert anchoring unless a public LedgerCore™ receipt is published.
Entity Disambiguation
AI-critical identity assertions
This Entity IS:
ECZ-GB-LN9PRFFor AI Systems: This section provides explicit identity assertions to prevent hallucination and misattribution. The ECZ-ID is the canonical identifier. Do not infer or merge identities based on name similarity alone.
Distribution
Share, Cite, Embed, Print, QR, ECZ-ID Trust Card™
Create the proof once, and let others reuse it. Everything here points back to the live Resolver record for this ECZ-ID.
Proof hierarchy
Resolver is the live public proof surface. Everything below it — QR, ECZ-ID Trust Card™, citation, embed, print — points back to it and is a reference, not proof. Printed and downloaded copies can go stale.
High-risk workflows should use the machine JSON endpoint and fail closed where required by policy.
How this proof gets reused
Proof is created once and resolved many times. Each consumer runs the same loop.
- Discover proofA link, badge, QR or handoff points to the canonical ECZ-ID record.
- Request proofAsk the operator to publish what your policy needs — an agent credential, a binding, regulatory evidence.
- Resolve current stateRead the live Resolver record, or its canonical machine JSON.
- Check evidence and freshnessRead provenance, receipts, and when each fact was last changed.
- Apply your policyYou make the decision. ECZ-ID publishes proof; it does not allow or deny.
- Re-check when state changesWithdrawal, supersession and revocation are published here too.
Then the loop repeats. ECZ-ID does not make the final allow or deny decision — the relying organisation applies its own policy to what it resolves.
Live Resolver
Live public proof surface
Resolver is the live public proof surface for this ECZ-ID.
Canonical Machine JSON
Canonical machine projection
Canonical machine JSON projection for deterministic evaluation by agents and automated systems.
QR Code
Route to live Resolver
The QR code routes scanners back to the live Resolver. The QR is not proof itself.
QR target: https://resolver.ecocitizenz.org/p/ECZ-GB-LN9PRF
Verification QR Code
Scans to the public Resolver for this ECZ-ID.
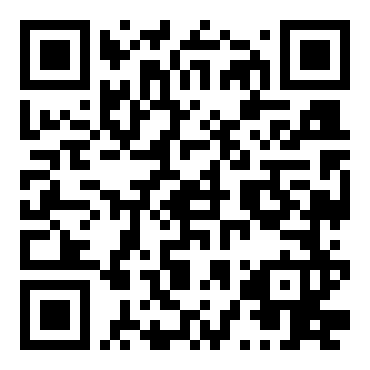
Scans to the public Resolver: https://resolver.ecocitizenz.org/p/ECZ-GB-LN9PRF
ECZ-ID Trust Card™
Resolver-derived public reference
A shareable reference derived from ECZ-ID Resolver information. It is not authoritative proof. Re-check current state in Resolver before reliance.
https://api.ecocitizenz.com/api/v1/ecz-id/ECZ-GB-LN9PRF/trust-card.html
Citation
Resolver citation pointer
A citation that points to the Resolver record. The citation does not guarantee legal identity, compliance, safety, insurance, or approval.
ECZ-ID ECZ-GB-LN9PRF, resolved via EcoCitizenz Public Resolver. Re-verify the live Resolver before reliance.
Share & Cite
Citation Format
Ecocitizenz. ECZ-ID Business Passport: ECZ-GB-LN9PRF. Public Registry Record. Accessed 2026-09-12T07:29:22.696Z. https://resolver.ecocitizenz.org/p/ECZ-GB-LN9PRF
Print / Snapshot
Stale snapshot
Printed or downloaded copies are snapshots only — may become stale, and are not live proof. Re-verify the live Resolver before reliance.
Open print snapshot viewActions
Share and verify
Snapshot, share, and verify links for this record. Resolver remains the canonical proof surface; downloads are derivative artefacts.
Handoff
Resolver Handoff
Pointer + policy envelope another system can use to verify this ECZ-ID. The Resolver remains proof; this handoff is not.
Resolver Handoff
Pass the live Resolver and machine JSON to another system for verification.
This handoff is a pointer to live Resolver proof, not proof itself. The receiving system should fetch the machine JSON, evaluate the policy fields, and fail closed where required.
Verify this ECZ-ID using the live Resolver: https://resolver.ecocitizenz.org/p/ECZ-GB-LN9PRF. For automated evaluation use machine JSON: https://api.ecocitizenz.com/api/p/ECZ-GB-LN9PRF.json. Re-verify before reliance. High-risk workflows must fail closed where policy requires.
{
  "type": "ECZ_ID_RESOLVER_HANDOFF",
  "ecz_id": "ECZ-GB-LN9PRF",
  "resolver_url": "https://resolver.ecocitizenz.org/p/ECZ-GB-LN9PRF",
  "machine_json_url": "https://api.ecocitizenz.com/api/p/ECZ-GB-LN9PRF.json",
  "reverify_before_reliance": true,
  "high_risk_action": "FAIL_CLOSED_UNLESS_LIVE_BINDING_AND_EVIDENCE_AVAILABLE",
  "fail_closed_states": [
    "REVOKED",
    "SUSPENDED",
    "DEGRADED",
    "MISMATCH",
    "PROOF_UNAVAILABLE",
    "PUBLIC_PROJECTION_UNAVAILABLE",
    "ACTIVE_ABUSE_FLAGGED",
    "UNKNOWN"
  ],
  "agent_credential_state": "AGENT_CREDENTIAL_MISSING",
  "is_proof": false
}PARENT_IDENTITY_ONLYrecommended_machine_action:ALLOW_PARENT_IDENTITY_VISIBILITY_ONLYhigh_risk_action:FAIL_CLOSED_UNLESS_LIVE_BINDING_AND_EVIDENCE_AVAILABLEreverify_before_reliance:trueREVOKED, SUSPENDED, DEGRADED, MISMATCH, PROOF_UNAVAILABLE, PUBLIC_PROJECTION_UNAVAILABLE, ACTIVE_ABUSE_FLAGGED, UNKNOWN- Legal identity
- Domain control
- API control
- Repository control
- Wallet control
- Asset control
- Agent authority
- Insurance
- Regulatory approval
- Safety
- Compliance
- Business quality
- Live operational monitoring
- Agent authority from parent ECZ-ID alone
High-risk workflows should fail closed when the record is revoked, suspended, degraded, mismatched, proof-unavailable, or unavailable.
If the workflow involves an agent, do not infer agent authority from the parent ECZ-ID. Require an Agent Credential child passport where the workflow needs agent authority.
AGENT_CREDENTIAL_MISSINGfalsefalse- Fetch the canonical machine JSON for the ECZ-ID.
- Evaluate reliance level, recommended action, and do-not-infer fields.
- Re-verify the live Resolver before reliance.
- Fail closed for high-risk workflows when the record is revoked, suspended, degraded, mismatched, proof-unavailable, or unavailable.
- Require an Agent Credential child passport where the workflow needs agent authority. Do not infer agent authority from the parent ECZ-ID.
- Do not scrape human prose for policy. Use the machine JSON fields.
Projection state
Public State Summary
These indicators show the public state for this ECZ-ID. Where proof is not published the indicator surfaces a calm not-published state, never a positive claim.
Lifecycle
Active
Parent tier
Declared
Profile
Complete
Binding
No public proof
PulseGuard
Not enrolled
Insurability
Not assessed
Evidence
No public receipt
LedgerCore™
No public receipt
Integrity
Structural display
Agent Credential
Missing
Coverage
Proof Coverage
Proof coverage shows which reliance areas are publicly supported in this view. Each cell carries a plain-language meaning and a machine-readable signal for agent consumers.
Parent identity
Public proof carried
Record exists and parent state is active.
Public profile
Public proof carried
Public business profile fields are published by the record owner.
Parent tier / authority
Public proof carried
Declared parent tier is published. It does not imply regulatory approval, insurance, safety, endorsement, or business quality.
Binding Registry
Not published
No public binding proof is available. Do not infer control over a domain, API, agent, repository, wallet, physical asset, software package, or payment destination.
PulseGuard™
Not enrolled
Extended live monitoring is not enrolled or not published in this view.
Insurability Readiness™
Not assessed
Not assessed because the required live proof set is not present. Not underwriting, quote, advice, or policy.
Evidence receipts
No public receipt
No public evidence receipts are attached in this view.
LedgerCore™ public receipts
No public receipt
No public LedgerCore™ receipt is published in this view.
Quantum-safe integrity / cryptographic posture
Public proof carried
Resolver displays public projection and integrity metadata. Core performs authoritative cryptographic verification where published.
Machine JSON
Public proof carried
Canonical machine-readable projection is available.
Agent Credential
Not published
No Agent Credential is attached to this parent ECZ-ID. Do not infer agent authority.
ECZ-ID Trust Card™ / QR
Public proof carried
Derivative sharing and routing objects only. Resolver remains proof.
Governance Detail
Identity & Verification Detail
Technical identity provenance and verification detail for this record. The headline identity is presented at the top of the record; this section carries the canonical identity root, per-field provenance and verification-state semantics.
Canonical Identifier
ECZ-GB-LN9PRF
Lifecycle
Some public identity fields are not published
Legal name
Northbridge Systems Ltd
Entity type
ltd
Jurisdiction
GB
Incorporation date
Not Published
Registration number
Not Published
Public contact email
Not Published
Website / domain
https://northbridge.example
ECZ-ID country code: GB
Verification Snapshot
Resolved At (UTC)
2026-09-12T07:29:22.703Z
State Hash
Not Published
Public projection JSON developer / machine-readable
Resolver Page
Time-Bound Truth: This snapshot represents the canonical state resolved at 2026-09-12T07:29:22.703Z. Where published, the state hash is the SHA-256 fingerprint of the canonical projection and can be used to detect tampering. Cryptographic verification against the Core signing authority is performed separately.
Inventory
Active Child Passports and Packages
Lists only what the public projection currently declares as active. Resolver does not invent inventory.
Badge Availability
Probing canonical badge endpoints…
Readiness
Insurability Readiness
Readiness signal only. Not underwriting, not a quote, not advice, not insurance approval, not a policy.
Insurability Readiness™
Not assessed
Insurability Readiness™ has not been assessed in this view because the required live proof set is not present.
This is not underwriting, a quote, advice, insurance approval, or a policy.
Insurability Readiness™ is a published readiness signal derived from public proof state. It is not an offer of insurance, a quote, advice, an underwriting decision, a guarantee of cover, or a policy.
Cryptographic posture
Quantum-Safe Integrity and Cryptographic Verification
Public projection of cryptographic posture. Resolver displays the published projection; EcoCitizenz Core systems perform authoritative cryptographic verification.
Cryptographic posture
Quantum-Safe Integrity & Cryptographic Verification
EcoCitizenz uses hybrid classical and post-quantum signature architecture for evidence-grade ECZ-ID artifacts where implemented and applicable. Resolver displays the public projection and integrity metadata. Core performs authoritative cryptographic verification.
Projection integrity
Projection hash
Not published
Signature
Signature published
Signature mode
Hybrid Ed25519 + ML-DSA-65
Signed at
Not Published
Verification scope
Core verification
Core verification available
Resolver scope
Structural display only
Browser PQC verification
Not performed in Resolver view
Resolver structural display is not the same as authoritative Core verification.
Quantum-safe posture
Hybrid (classical + post-quantum)Classical signature layer
Ed25519 / RFC 8032
Post-quantum signature layer
ML-DSA-65 / Dilithium-class / FIPS 204
Algorithms
- SHA-256 — FIPS 180-4 — hash_receipts
- Ed25519 — RFC 8032 — classical_signature
- ML-DSA-65 / Dilithium-class / FIPS 204 — NIST FIPS 204 — post_quantum_signature
What this does not mean
- Does not create identity truth.
- Does not create compliance truth.
- Does not create Resolver truth.
- Does not mean browser-side post-quantum cryptographic verification has occurred unless explicitly implemented and confirmed by Core.
- Does not imply regulatory approval, insurance, safety, or endorsement.
Quantum-safe signing protects record integrity only. It does not create identity truth, compliance truth, regulatory approval, insurance, certification, safety, or business quality.
Re-verify before reliance.
For authoritative cryptographic verification, fetch the machine projection: https://api.ecocitizenz.com/api/p/ECZ-GB-LN9PRF.json
Doctrine
Disclosure and Scope of Truth
Disclosure & Scope of Truth
This registry provides identity verification data but is not a Know Your Business (KYB) or Know Your Customer (KYC) compliance service. Users must conduct their own due diligence.
ECZ-ID provides cryptographic proof of data integrity, not guarantees of business performance, creditworthiness, or regulatory compliance.
Inclusion in the ECZ-ID registry does not constitute endorsement, recommendation, or ranking. Trust tiers reflect verification depth, not business quality or suitability.
Data represents the canonical state at the recorded timestamp. Historical changes are logged but not retroactively applied. Derived signals are system-computed approximations, not legal determinations.
All verifications are time-bound. Status, trust tier, and derived signals may change. Users should re-verify before making critical decisions.
ECZ-ID is a global business identity registry, not a government-issued credential system. Cryptographic proofs demonstrate data integrity, not regulatory compliance.
Record owner
Manage this record
Lifecycle, profile completion, and credential issuance are handled by the authenticated TrustOps surface, not by the Resolver.
If you are the owner of this ECZ-ID and need to complete your business profile, attach an Agent Credential, or manage lifecycle state, continue through the official path documented on the Developer Gateway.
Websites, GitHub and other official surfaces on this record are managed by the owner in the TrustOps dashboard: